SOC status:Duty analyst on shift

UK Cyber Defence

Insights

Answers, not alarms.

Research, detection engineering notes and plain-English explanations for the questions UK boards, IT managers and security leads actually ask. One substantial piece a week; a short threat brief in between.

Get the fortnightly briefing

Double opt-in. Unsubscribe in one click. No sharing, ever.

TopicsAdversary-in-the-middle 1Agentic AI 1AI in security 2AI security 1AI SOC 1Alert fatigue 1Banking 14Biometrics 1Board and governance 3Board governance 1Case study 4CISO 1Citrix NetScaler 1Cloud security 5Cold chain 1Compliance 5Consulting 1Cross-sector 3CSRF 1Cyber Essentials 1Cyber skills 1Danfoss 2Data breach 2Data protection 1
Insights

Cyberattack defrosts the fridges at hundreds of French supermarkets

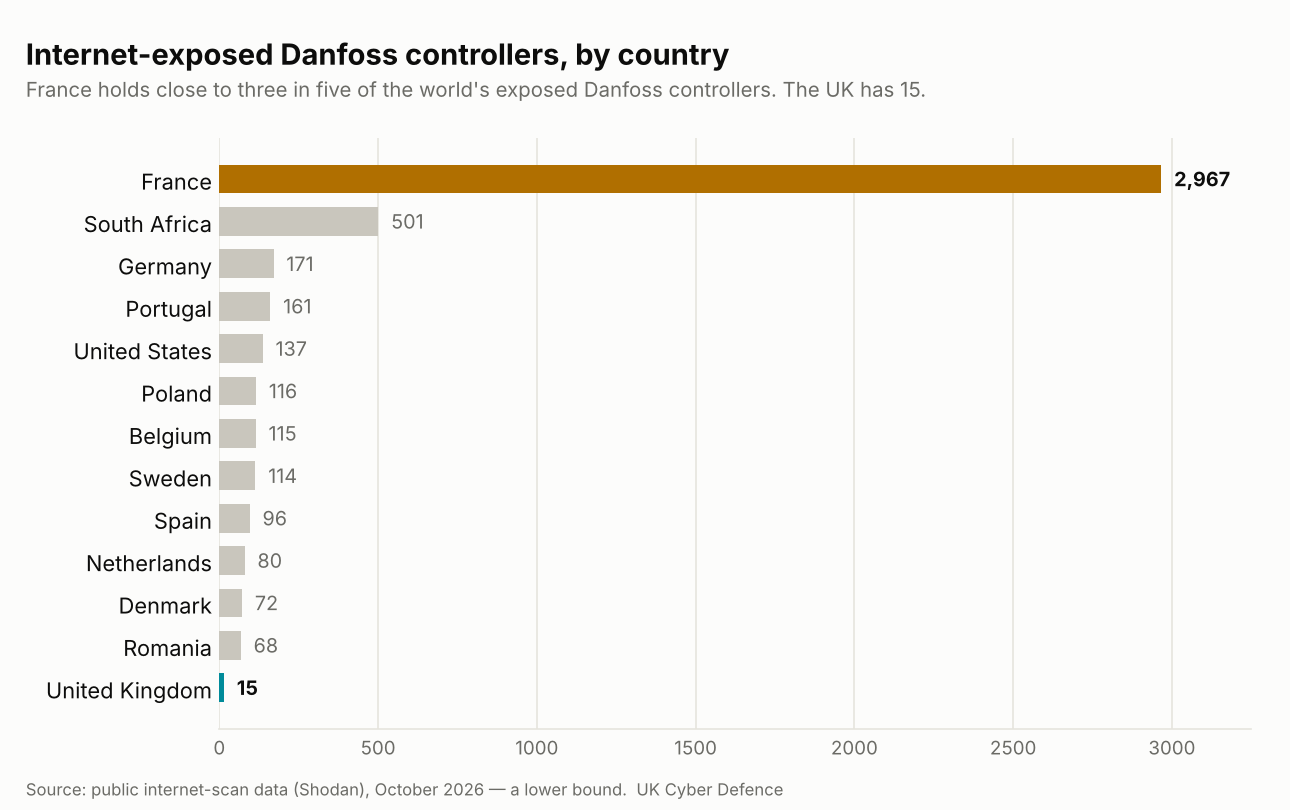
Overnight on 11–12 October 2026, attackers reached into the refrigeration controllers of several hundred French supermarkets and switched the fridges and freezers into a defrost cycle that never ended. Intermarché, Coopérative U, Carrefour and Leclerc lost their chilled and frozen stock, the Paris prosecutor has opened an investigation, and the equipment at the centre of it is sitting on the open internet in the UK too.

Peter Bassill11 min read · 174 reads
Insights

Citrix NetScaler again: two exploited zero-days, and why patching is only half the job

Two critical flaws in Citrix NetScaler ADC and Gateway are being exploited in the wild, both scored 9.5, both reachable by an unauthenticated attacker on the internet-facing side of the box. CISA has given federal agencies until 30 September. Here is what the flaws are, why the honest instruction from several national authorities is to take the appliance offline, and why installing the update does not, on its own, get an intruder out.

Peter Bassill10 min read · 33 reads
Insights

Seeing what your SOC sees: the new SIEM section in Pulse

Managed security has a quiet flaw: when it works, there is nothing to look at. The latest release of Pulse, our client portal, changes that. You can now watch the activity our Security Operations Centre records across your estate as it happens, see every monitored machine, and open the same page for each one that our analysts use. Here is what has changed, why we built it this way, and how to get the most from it.

Peter Bassill19 min read · 6 reads
Insights

500,000 faces, one false alarm: what the rail facial-recognition trial really tells us

British Transport Police scanned more than half a million faces at London stations over six months. The system raised a single alert, and it was wrong. Before this is filed under 'surveillance that failed', it is worth understanding why the numbers came out as they did, because the lesson is not the one either side is shouting, and it applies to any organisation thinking about biometrics.

Peter Bassill10 min read · 5 reads
Insights

The phishing page that let Microsoft do the reconnaissance

I spent a few minutes yesterday poking at a phishing page that behaved exactly like the real Microsoft 365 sign-in, because it was the real Microsoft 365 sign-in, relayed through the attacker's server. What made it worth writing about was not the theft of credentials but the quiet way it used Microsoft's own sign-in endpoints to work out, before a password was ever typed, whether it had caught a real account at the right company.

Peter Bassill13 min read · 12 reads

229 articles · page 1 of 20